Static & dynamic security testing
for iOS, right on your Mac.
IPAScope scans an .ipa or .app bundle for
security issues — entirely on your Mac, entirely offline. No account, no
backend, no upload. Point it at a build and get MASVS-mapped findings in
seconds, plus an optional AI-written pentest report. Prefer the terminal?
The same engine ships as a CLI too.
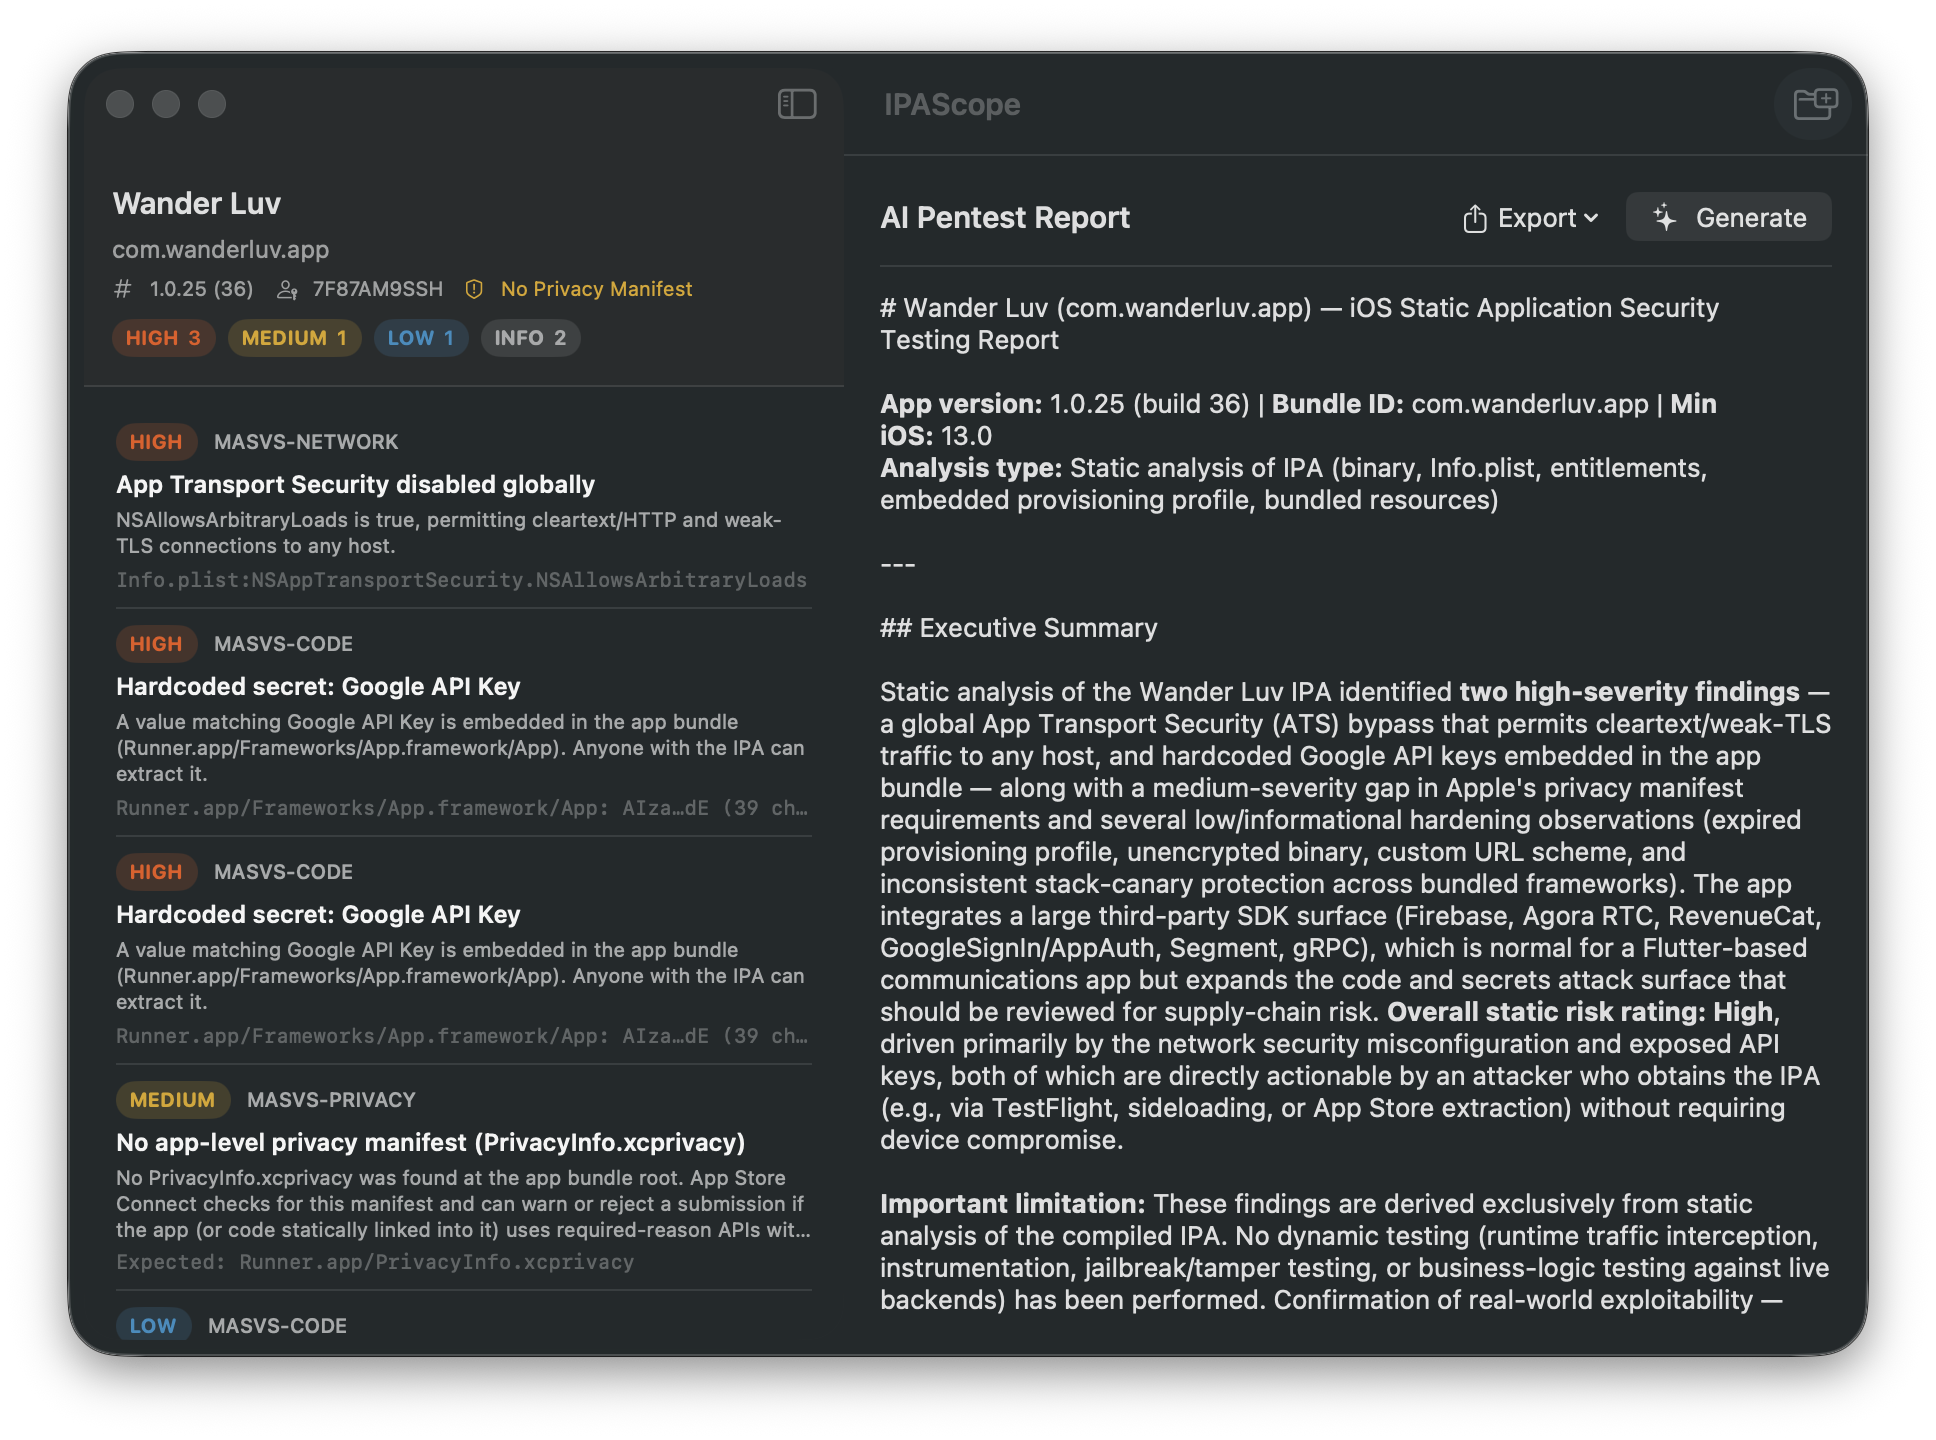
37 checks run · 2 High · 6 Medium · 9 Low · MASVS-mapped
From IPA to report in minutes
Drop in your build
.ipa or .app. Nothing leaves your Mac.
IPAScope scans it
Entitlements, binaries, SDKs, secrets, privacy manifests, hardening.
Review MASVS findings
Severity-ranked, with evidence for every result.
Export a report
SARIF for CI, or an AI-written pentest report for clients.
What it checks
Info.plist & entitlements
App Transport Security (global and per-domain cleartext exceptions),
permission purpose strings, custom URL schemes, background modes,
provisioning profile expiry and get-task-allow.
Binary hardening
FairPlay encryption status, PIE/ASLR, stack canaries, arm64e pointer authentication, and linked dylibs — across fat and thin Mach-O binaries.
Third-party SDKs
Trackers, ads, analytics, and crash-reporting SDKs detected from an
offline signature list, cross-referenced against each SDK's own
PrivacyInfo.xcprivacy manifest.
Hardcoded secrets
AWS, GCP, Stripe, Slack, and GitHub keys, private keys, and JWTs — detected in the bundle. Only a redacted preview is ever stored; raw secrets never leave your machine.
Embedded endpoints
Hardcoded URLs pulled from the main executable and every embedded framework — staging APIs, internal hosts, and debug endpoints left in a production build, filtered clear of boilerplate noise.
Weak cryptography
MD5, SHA-1, DES, and ECB-mode usage flagged wherever they appear — broken or weak primitives that shouldn't be protecting anything security-sensitive.
Known-vulnerable SDKs
Detected third-party frameworks are version-checked against a bundled CVE database, so an outdated, exploitable dependency doesn't slip through unnoticed.
Certificate pinning vs. ATS
Flags the specific combination that matters: App Transport Security disabled and no certificate-pinning code detected, meaning traffic has no integrity check at all.
Native/JavaScript bridges
Detects WKScriptMessageHandler usage exposing native
functionality to a WKWebView — and flags it as high severity when it's
also reachable over a connection ATS was told to leave insecure.
Built for people who actually test iOS apps
Pentesters
Get useful findings without digging through scanner noise.
AppSec teams
Check an app's security posture before a build reaches production.
iOS developers
Catch insecure configuration, exposed secrets, and binary-hardening gaps early.
Security consultants
Turn a scan into MASVS-mapped evidence and a client-ready report.
Same engine, in your terminal
Everything above is also available as ipascan —
for CI pipelines, scripting, or auditing a whole portfolio of client apps at once.
$ ipascan WanderLuv.ipa
Scanning WanderLuv.ipa …

IPAScope report — Wander Luv
  Bundle:  com.wanderluv.app
  Version: 1.0.25 (36)
  SDKs:    Google Firebase, Segment

  HIGH 3   MEDIUM 2   LOW 1   INFO 3

  HIGH    [MASVS-NETWORK] App Transport Security disabled globally
  MEDIUM  [MASVS-CRYPTO]  Weak cryptographic API usage detected
           references CC_SHA1 in FirebaseInstallations
  INFO    [MASVS-NETWORK] 79 embedded network endpoint(s) found

$ ipascan WanderLuv.ipa --sarif > results.sarif        # GitHub / GitLab code scanning
$ ipascan ./client-builds --diff --json > report.json  # batch-scan a directory, new findings only
- SARIF export —
--sarifemits SARIF 2.1.0, the format GitHub, GitLab, and Xcode Cloud ingest natively for PR annotations. - Diff mode —
--diffreports only findings new since the last scan of a given bundle ID, for recurring review across releases. - Batch scanning — point
ipascanat a directory of.ipa/.appfiles to audit a whole client portfolio in one run. - Never breaks your build —
ipascanalways exits0on a completed scan. It's built to inform your pipeline, not gate it.
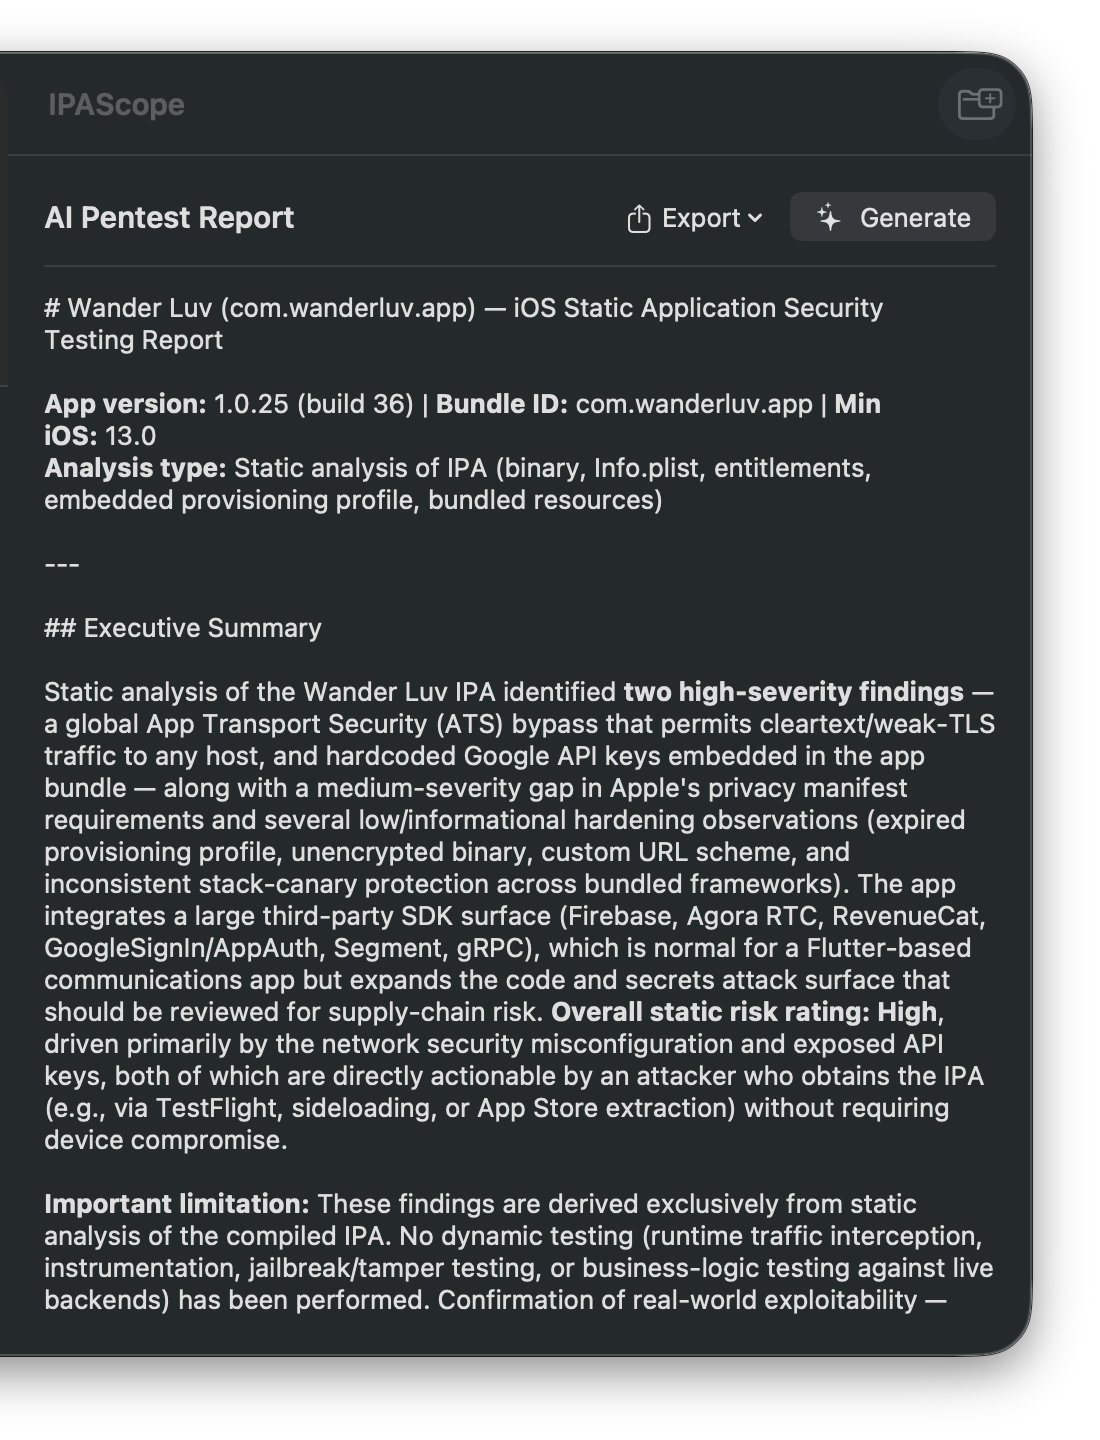
An AI pentest report, using your own key
Every finding is mapped to an OWASP MASVS category and ranked by severity. Generate a full written report on demand — only redacted evidence is sent, directly from your Mac to the provider you configure, using an API key you supply. IPAScope never sees it.
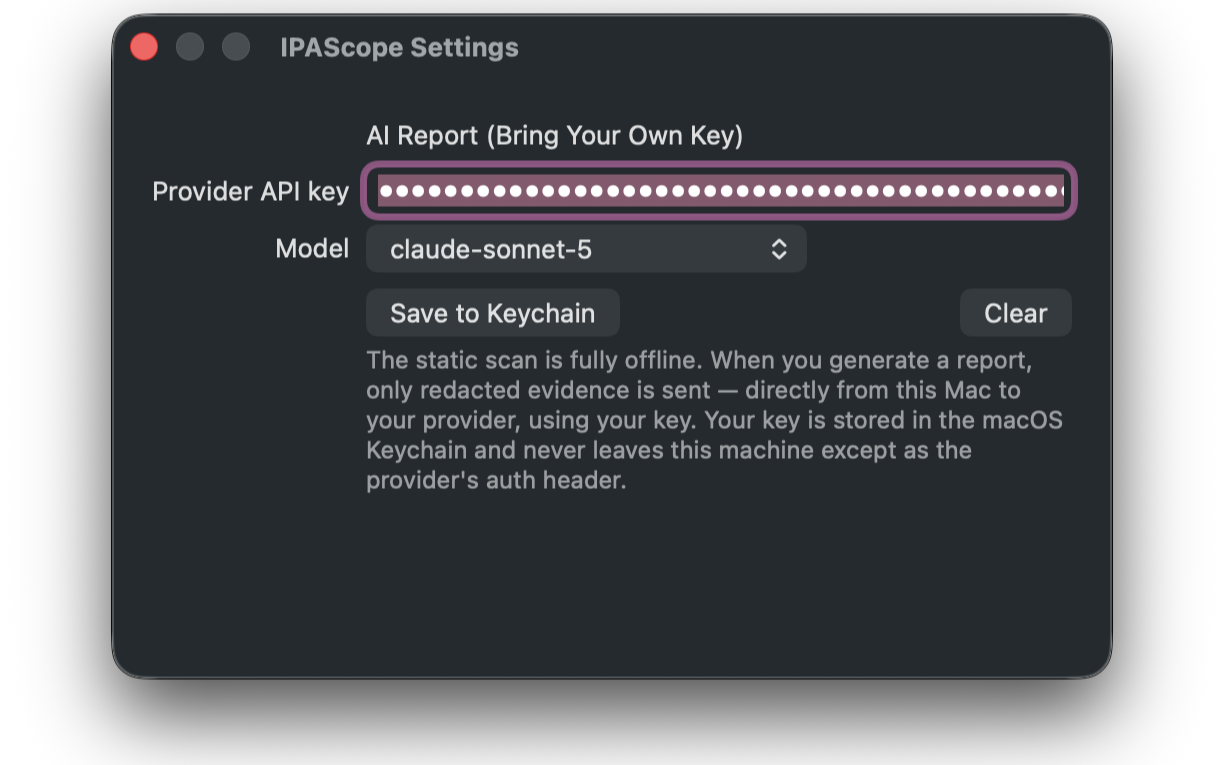
Bring your own key
Your key is stored in the macOS Keychain and never leaves this machine except as the provider's auth header. There's no IPAScope backend to trust — the static scan is fully offline, and the report step is a direct connection you control.
Pricing
IPAScope Pro
$129 one-time
Full static & dynamic analysis, the ipascan CLI, and
AI report generation — unlocked at download, no subscription, no
account. Free updates.